
For U.S. defense contractors
Your cybersecurity score is a claim.
We make it provable.
Sign your next affirmation knowing the number holds.
Muse helps defense contractors find the gaps an assessor would find, and see what their AI tools can reach, before anyone checks.
Led by Dr. Linda Cureton, former Chief Information Officer of NASA.
60 minutes with a certified CMMC professional and Dr. Cureton. No system access. No recording. No copies of your documents.
System Security Plan
No dated exercise record.
Built for defense contractors that handle CUI, post a score in SPRS, and have a senior official sign it every year.
Most SPRS scores have never been checked.
You scored yourselves.
Often years ago, often by someone who has since moved on.
A senior official signs it every year,
affirming that the score is accurate.
Someone will check it.
A prime, the government's own assessors, or someone inside your company.
One public case
110
-170
- No breach
- No whistleblower
- Settled a False Claims Act case in June 2026
A control you can't prove doesn't count.
Assessors don’t score what you have. They score what you can show: a current plan, a dated record, a named owner. Three things can stop an assessment whatever your score says.
An out-of-date security plan
Without a current System Security Plan, an assessment can’t be completed.
CUI outside your boundary
Controlled files on shared drives, in unlisted cloud apps, or in email archives your plan doesn’t cover.
A score that doesn’t match
A posted score your records can’t support, or open items the rules don’t allow on a plan of action.
Try three right now
The same three questions Dr. Cureton asks in the room. Answer honestly. "Not sure" counts as no.
-
1. Could you open your System Security Plan in the next ten minutes, and does it describe the system as it runs today?
-
2. Can you name every place your CUI lives, including cloud apps and AI tools, and is each one inside your boundary?
-
3. If someone recounted your score from your plan today, would they land on the number you posted?
Your AI can already read your CUI.
If your team uses Microsoft Copilot or a similar tool, it can find and summarize anything its users can open.
If controlled files sit in a folder with loose permissions, the AI will surface them to anyone who asks. Your boundary moved, and nobody decided it should.
Asked by a new hire in marketing
"Summarize our latest work for the Navy."
How we help, one step at a time
You only ever decide on the next step.
1
SPRS Score Check
Sixty minutes on a screen share. You leave with the three things to fix first.
2
CUI and AI Exposure Review
Six weeks. Every one of the 320 assessment objectives gets a named owner and evidence source, and we document what your AI tools can reach. Under 10 hours of your team’s time.
Guarantee: every objective comes back with a named owner and evidence source, or we don’t invoice.
3
Build
We close the gaps and set up evidence that stays current as part of normal work.
4
Ongoing support
We keep it true as people, systems and AI tools change, ready for every yearly affirmation.
Every engagement is a fixed fee, agreed on a call. No software to buy.
Your IT provider runs the controls. We make them provable.
We work alongside your IT provider, not instead of them, and hand them a clearer list of what’s needed.
We come from federal records, not cybersecurity.
We sell nothing else.
Your evidence stays yours.
We never claim to certify.
Only an authorized assessor certifies. We make sure your evidence holds up when one looks.
NASA
Former CIO leads the firm
1M+
Federal case records managed
7
Federal agencies served
ISO 9001
Certified quality framework
2013
Year established
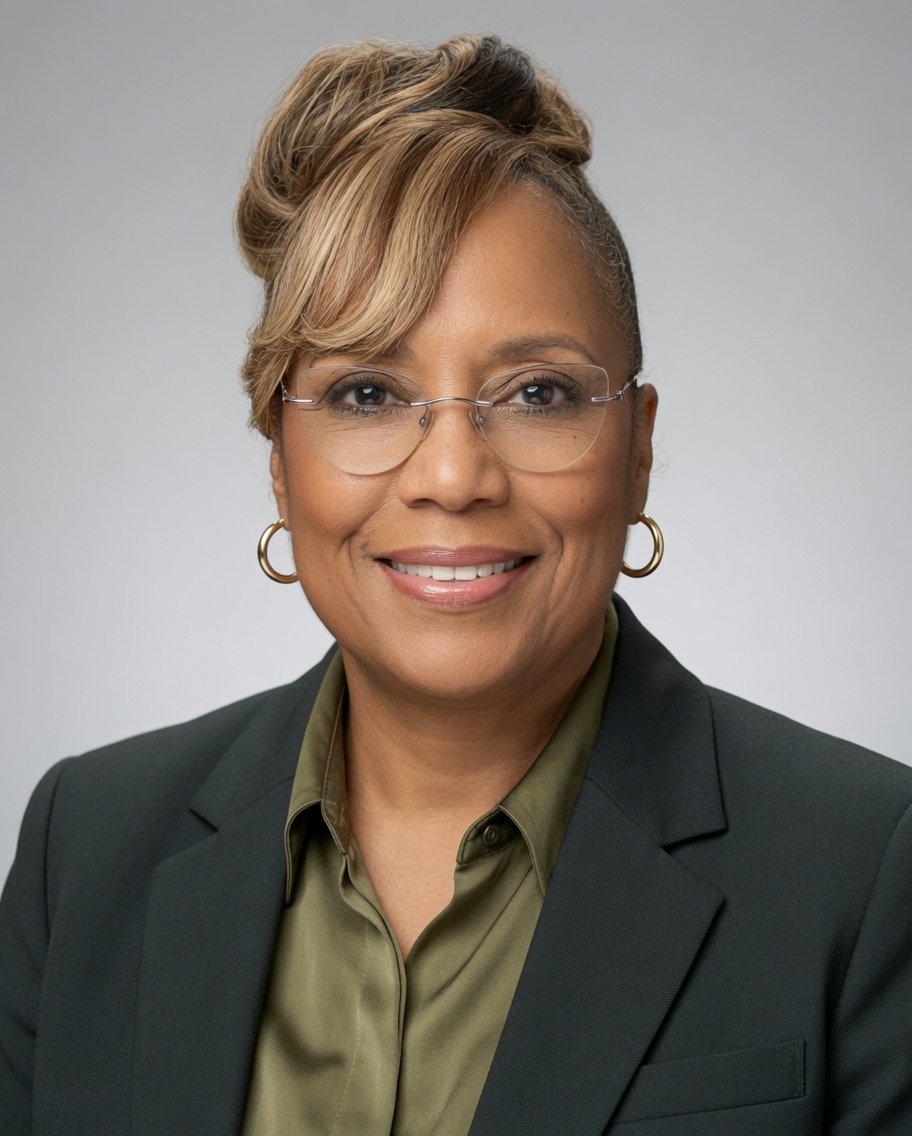
Dr. Linda Cureton
“Meaningful transformation takes two things in equal measure: visionary leadership and the discipline to execute.”
Find the gaps in your SPRS score before someone else does.
- 1. Your System Security Plan
- 2. Your posted SPRS score
- 3. Your plan of action
- 1. Where your score is likely to break
- 2. What you can fix yourselves
- 3. The three things to fix first, in writing
Best booked before your next SPRS affirmation, or before a prime asks for your score.
Your fix list
1
It still lists a file server retired in 2023 and leaves out two cloud apps. An assessor stops here. Your team can fix this.
Drawings sit on a shared drive your plan doesn’t cover, and Copilot can reach it. Needs help.
Shown for email only. Worth 5 points if not met. Your IT provider can fix this.
Not ready to talk yet?
Get the 10-point SPRS desk check: the ten questions our reviewers start with, on one page. Answer them at your desk in about 15 minutes.
Questions we hear
Isn't CMMC paused?
The third-party certification phase was paused in July 2026. The self-assessment, the score in SPRS, and the yearly affirmation are still required.
Our IT provider handles this.
Good. They run the controls. We make them provable, and we give your provider a clearer list of what’s needed. We don’t replace them.
Can you certify us?
No. Only an authorized assessor can certify, and nobody honest promises a result. We make sure your evidence holds up when an assessor looks.
Do you need access to our systems?
Not for the Score Check. You share your screen and we look. We don’t record the call or keep copies of your documents.
What does it cost after the Score Check?
The Score Check is free. Anything after it is a fixed fee based on your size and scope, agreed on a call before any work starts.
For federal agencies
A control you can't prove doesn't count.
Find the gaps before your next affirmation, not after someone else does.